Access for saleClosed forum · Dark web
A broker is selling VPN access to your network.
Working employee logins, offered to the highest bidder before anyone inside knows they leaked.
TAM-C · Verified and client alerted
We watch the dark web, leak sites and your digital surface for threats aimed at your organization. Then we tell you what is real, and what to do about it.
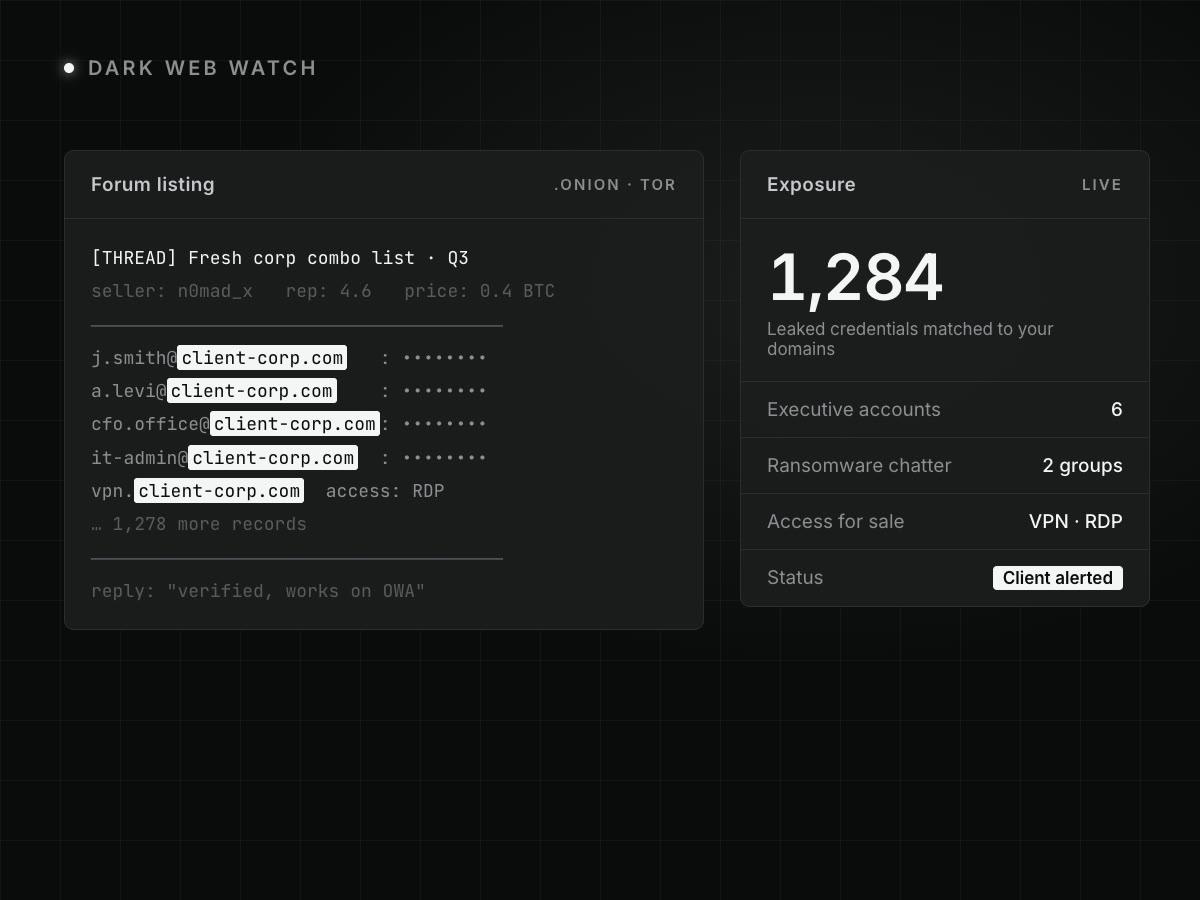
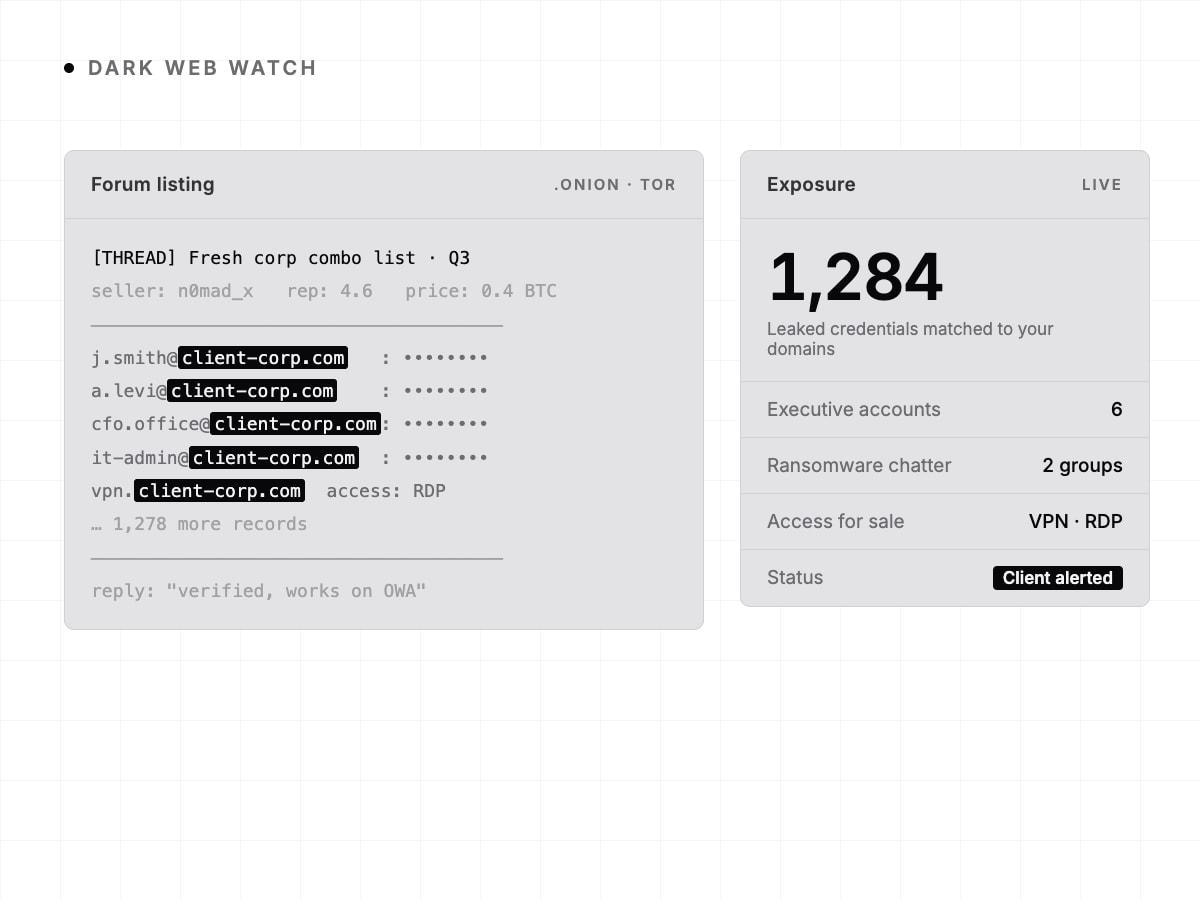
The warning signs of an attack usually appear on the dark web days or weeks before it lands: stolen logins for sale, your name on a leak site, a fake domain going live. Someone just has to be looking.
Working employee logins, offered to the highest bidder before anyone inside knows they leaked.
TAM-C · Verified and client alerted
Their stolen files include your contracts, your people and your pricing.
TAM-C · Verified and client alerted
The first step of a phishing campaign aimed at your finance team.
TAM-C · Verified and client alerted
Typical findings. Client details are never shared.
Analysts and our Deep Web System monitor dark and deep web forums, markets, leak sites and your digital surface around the clock.
Every finding is checked by a person for relevance, credibility and intent, so you only hear about what is real.
You get a clear alert with what was found, why it matters and what to do, through ARGO NG, email, SMS or your own systems.
We stay with you: investigation, takedown support, secure communications and, if it crosses into the physical world, people on the ground.
A leaked travel itinerary is a cyber finding until your executive lands. A threat on a forum is a cyber finding until someone turns up at the gate.
TAM-C runs cyber, physical and human intelligence in one operation. The analyst who spots the leak can call our 24/7 GSOC, open an investigation, or put a team on the ground. That is something software-only providers can't do.
Dark and deep web platforms watched for threats aimed at you.
Learn more →02Early warning on ransomware groups, leak sites and attacks on your brand.
Learn more →03Leaked and stolen databases evaluated against your people and domains.
Learn more →04Exposed devices and look-alike domains found before attackers use them.
Learn more →0524/7 monitoring of restricted infrastructure, run by our Tiger Team.
Learn more →06An outside-in rating of your cyber exposure, scored and explained.
Learn more →07Leaked credentials and complex datasets turned into answers.
Learn more →08Secure devices and apps for the conversations that can't leak.
Learn more →We look at your organization the way an attacker would and show you what is already exposed. From there, the Cyber Suite keeps watch, on its own or alongside our other suites.